Bash Scripting — TryHackMe
A complete beginner-friendly walkthrough of the Bash Scripting room — syntax, variables, parameters, arrays, conditionals and debugging, with a cheat sheet.
Read on MediumPenetration Tester | Web Application Security
I find and exploit security weaknesses in web applications and networks — before attackers do — and deliver clear, prioritized remediation that engineering teams can act on. Offense-driven. Remediation-focused.
Penetration tester with hands-on experience in web application security, vulnerability assessment, and network security testing. Skilled in OWASP Top 10 exploitation techniques and professional security reporting, with demonstrated ability through CTF competitions and controlled lab environments.
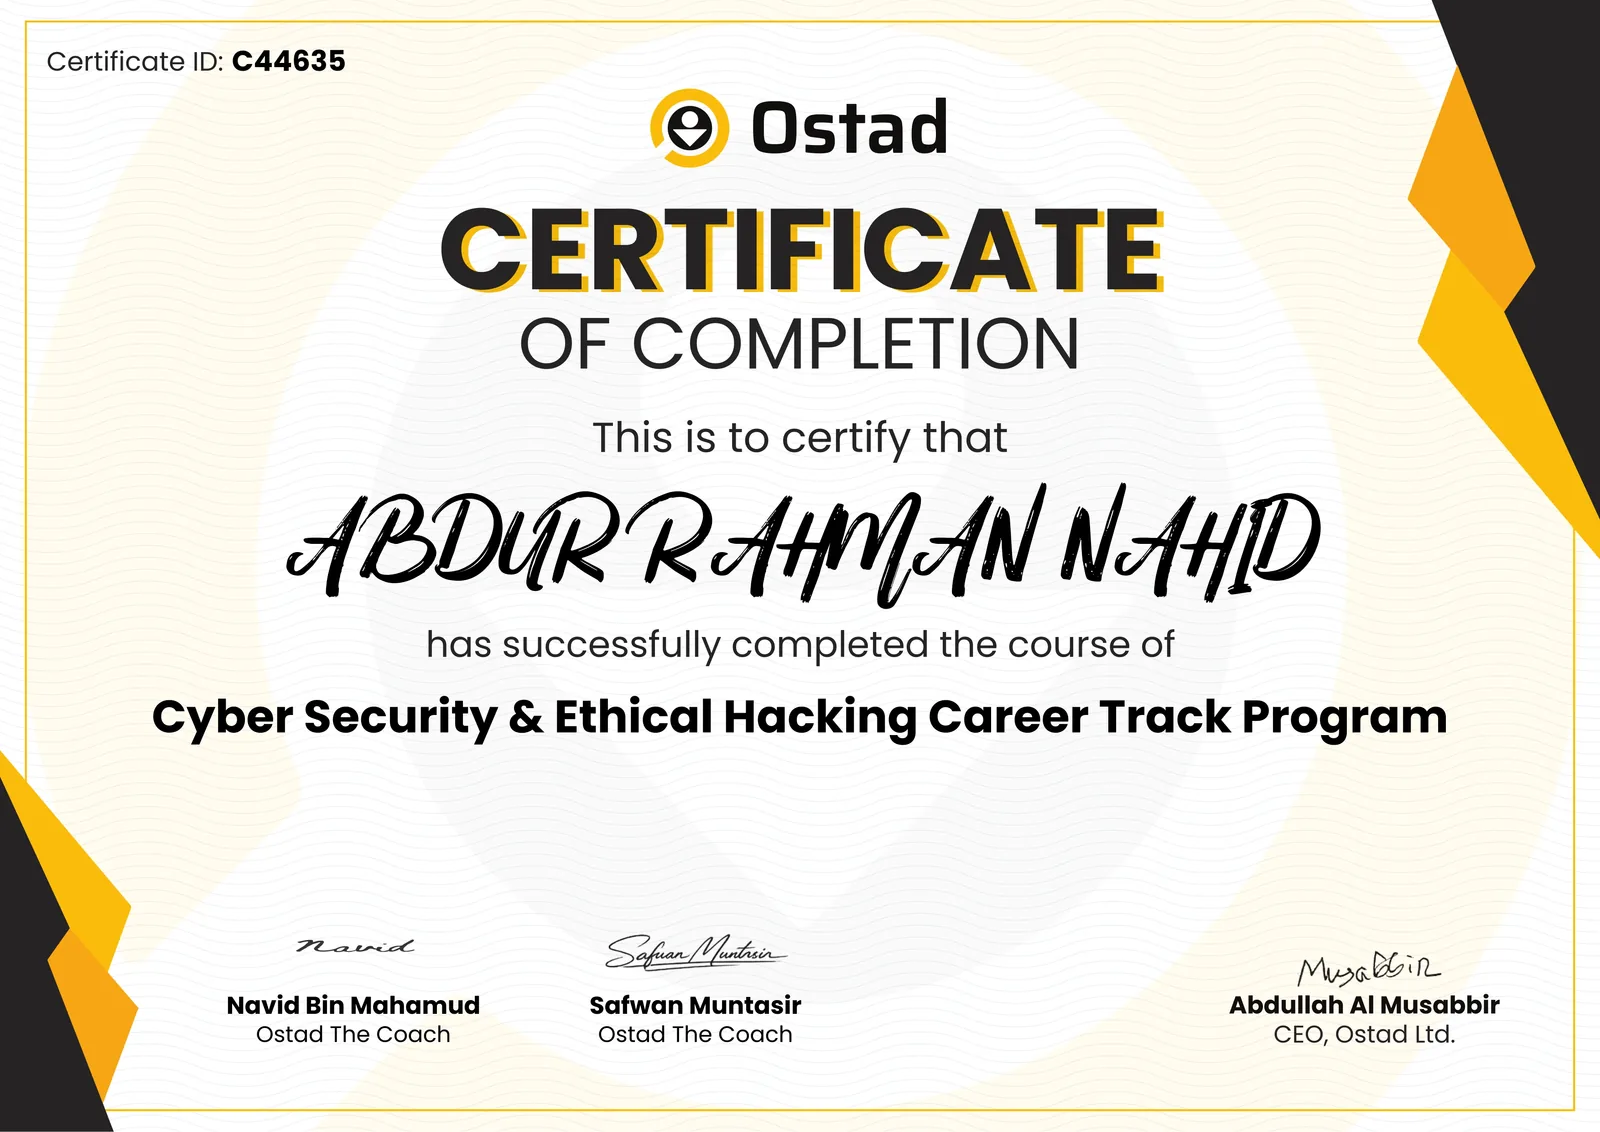
As an Apprentice in Cybersecurity & Ethical Hacking at Ostad, I apply the OWASP Testing Guide and PTES methodologies to every assessment — from reconnaissance to structured reporting with risk ratings and remediation recommendations.
I'm currently seeking an entry-level penetration testing or security analyst position where I can turn offensive findings into real defensive strength.
Every engagement follows OWASP & PTES — no guesswork, no missed attack surface.
Every finding is validated through actual exploitation in authorized, controlled environments.
Risk-rated findings with clear remediation steps developers can implement immediately.
Competed in multiple CTF events across web exploitation, network, and digital forensics categories. Published detailed technical writeups documenting attack methodology, tools used, and remediation guidance.
Conducted full security assessments on DVWA and WebGoat targeting SQL Injection, XSS, CSRF, and broken authentication. Used Burp Suite to intercept and manipulate HTTP traffic to identify and exploit security weaknesses.
Performed network reconnaissance, scanning, and post-exploitation using Nmap, Metasploit, and Wireshark in a controlled environment. Documented all findings in structured penetration test report format.
A complete beginner-friendly walkthrough of the Bash Scripting room — syntax, variables, parameters, arrays, conditionals and debugging, with a cheat sheet.
Read on MediumNo experience needed — if you can open a terminal, you can learn SSH. A practical introduction to remote administration, secure connections and file transfers.
Read on MediumNew walkthroughs, security notes and practical guides are published regularly on my Medium profile. Follow along for future posts.
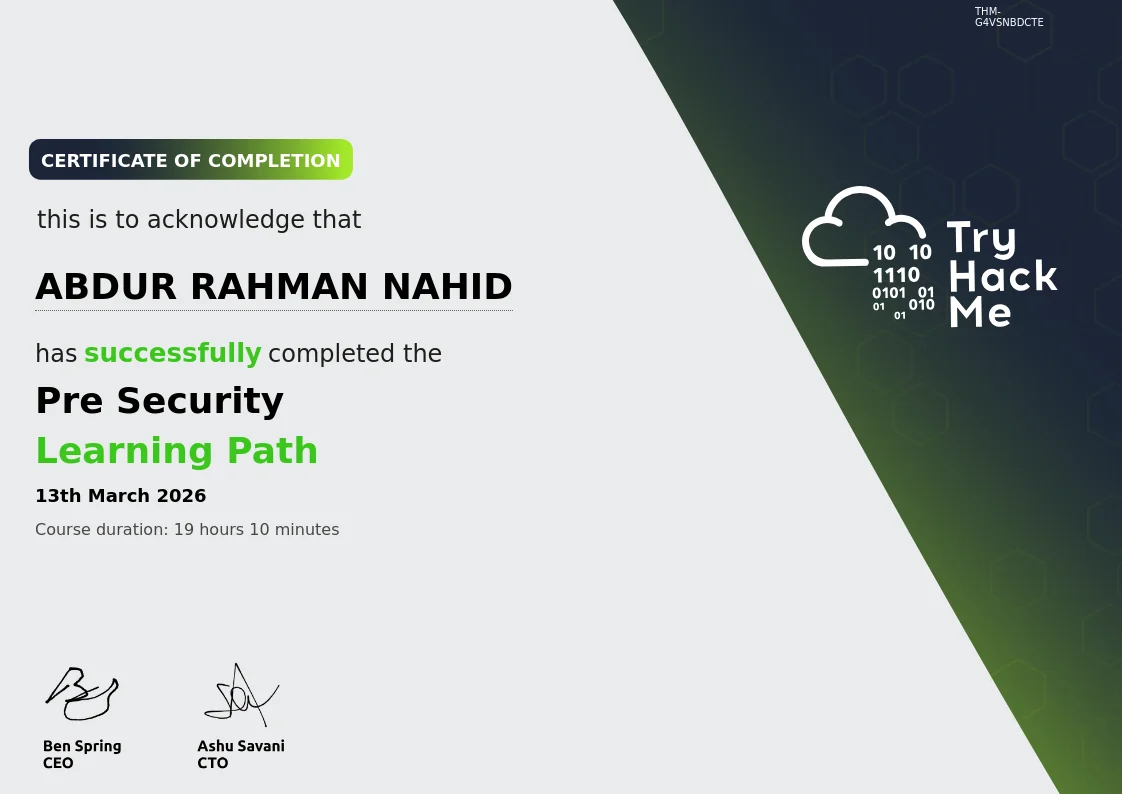
View all articlesFoundational security training covering networking, web fundamentals, and Linux — pathway into penetration testing.
View Certificate ↗Hands-on apprenticeship covering web app pentesting, network assessments, CTFs and professional reporting (OWASP & PTES).
Available for penetration testing engagements, vulnerability assessments, and entry-level security roles. Based in Dhaka, Bangladesh — working remotely worldwide.